Why a QR Code Is an Access Point, Not a Guarantee of Trust
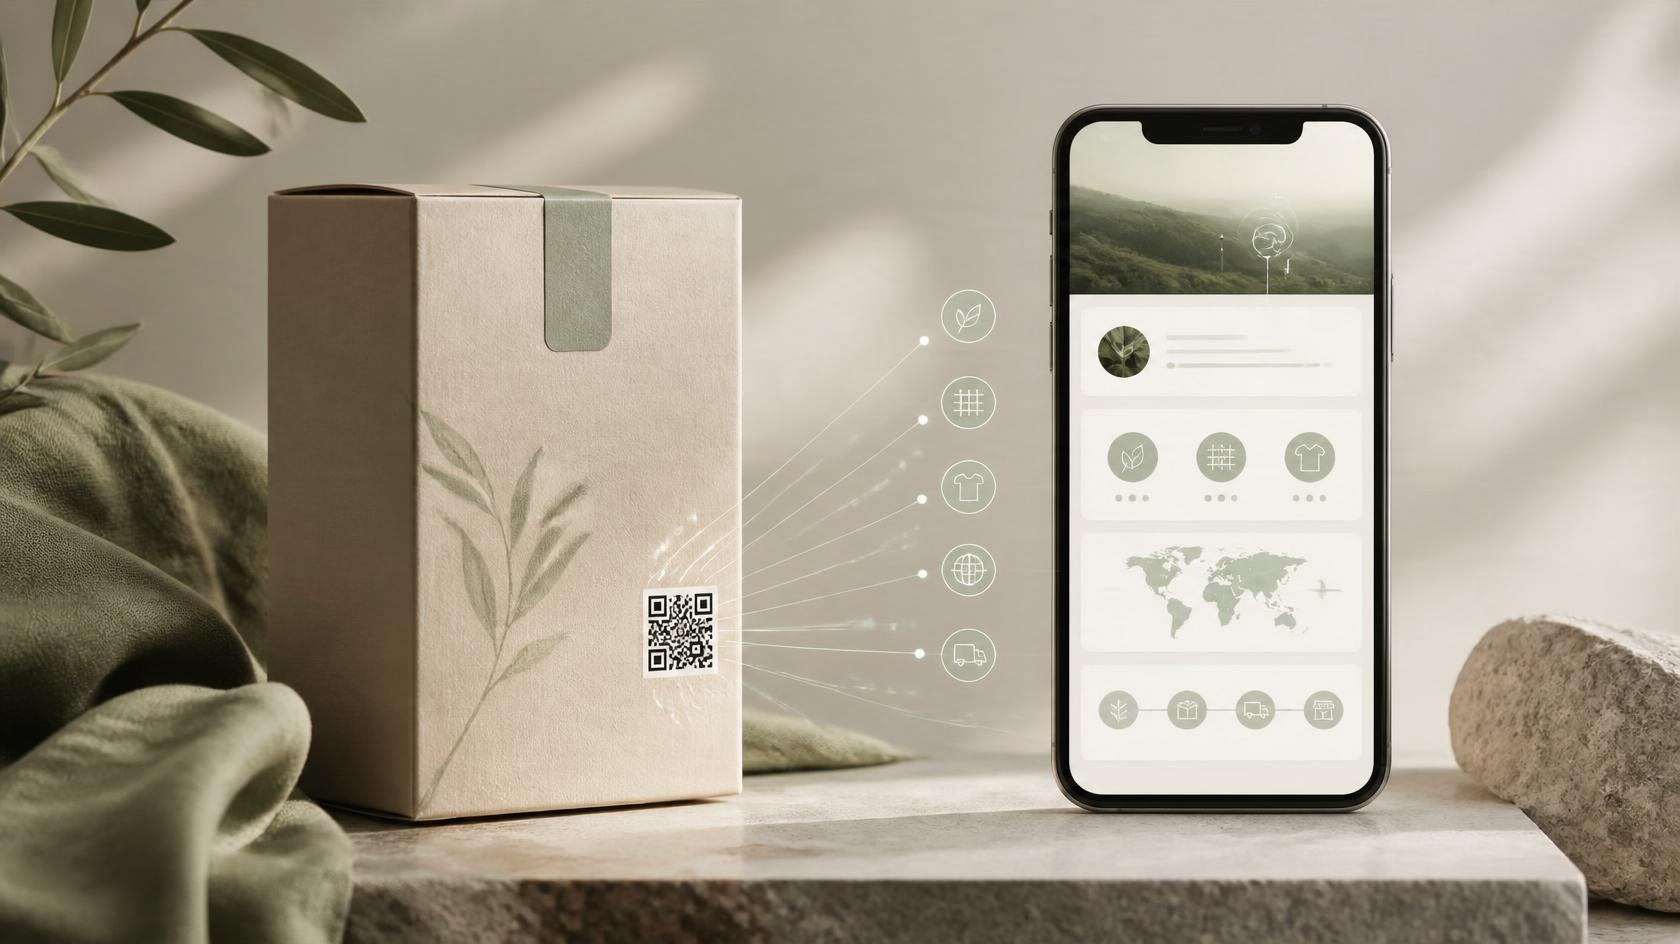
QR codes have become a familiar bridge between physical products and digital information. Used across packaging, payments, logistics and emerging applications such as the Digital Product Passport (DPP), they allow users and supply-chain stakeholders to access product data through a simple scan. The European Commission describes the DPP as a digital container designed to make product information available across the lifecycle and identifies the data carrier as the connection between the physical product and its digital record.
Yet this convenience conceals an important weakness. A QR code is readable by a device, but its destination and purpose are not immediately understandable to the person looking at it. Before scanning, users generally cannot determine whether the code leads to an official product record, a modified webpage or a deceptive digital environment. This creates an asymmetry of trust: the user is asked to act before the destination can be assessed.
This matters because the code itself does not validate the information it retrieves. It provides access to digital resources, but it does not automatically prove that the destination is authentic, that the data has not been manipulated or that the source is still controlled by the organization responsible for the product. NIST warns that phishing can use convincing messages and harmful links to direct users toward fraudulent environments, obtain sensitive information or trigger malicious downloads. Although a QR code changes the interface, the underlying risk remains the same: an apparently legitimate access point can conceal an untrusted destination.
In a traceability system, this distinction is critical. The QR code may be the first point of contact with information about a product’s origin, composition, compliance or end-of-life management. If that entry point is replaced, redirected or disconnected from a governed data source, even accurate information stored elsewhere in the system may no longer protect the user. The issue is therefore not whether QR codes are inherently secure or insecure, but whether the entire connection between the physical code, the digital destination and the underlying product data is protected.
Not all QR codes are equal because not all of them are supported by the same identification standards, domain controls, authentication mechanisms and data-governance processes. In traceability, trust cannot be embedded in the graphic symbol alone. It must be established across the complete chain linking the product to its verified digital identity.
When One Scan Opens the Wrong Door
The widespread adoption of QR codes has transformed the way people access information. A simple scan can connect a consumer to product specifications, compliance data, sustainability credentials, traceability records or digital services in seconds. However, the same mechanism that makes access frictionless can also create a hidden security challenge: users are often unable to assess where a QR code will lead before interacting with it.
Phishing Through Trusted-Looking Experiences
One of the most common risks associated with QR codes is their use as a vehicle for phishing attacks. Cybercriminals can replace legitimate codes or distribute fraudulent ones that redirect users to websites designed to imitate official platforms. Once there, users may be prompted to enter credentials, payment details or other sensitive information, believing they are interacting with a trusted source. Security guidance from NIST highlights that phishing attacks frequently rely on convincing links and trusted-looking interfaces to deceive users into disclosing information or taking unsafe actions.
In traceability environments, the consequences can be particularly significant. A counterfeit QR code attached to a product, shipment or document may not only mislead the user but also undermine confidence in the broader information ecosystem that organizations rely on to demonstrate authenticity and compliance.
Malware and Device Compromise
A second concern is the potential for QR codes to direct users toward malicious content. While modern operating systems have significantly improved their security controls, QR codes can still serve as a delivery mechanism for links that initiate unwanted downloads, redirect users to compromised websites or exploit vulnerabilities in outdated devices and applications. The risk does not originate from the QR code itself, but from the digital destination it references.
Because scanning is often perceived as a low-risk action, users may apply less scrutiny than they would when clicking a suspicious email link. This creates an opportunity for attackers to bypass normal caution and exploit the trust associated with physical products, packaging or printed materials.
Exposure of Sensitive Data and Connected Services
As digital ecosystems become increasingly interconnected, QR codes are no longer used solely to display information. They can also interact with authenticated applications, digital identity systems, payment platforms and product information services. In these contexts, a manipulated QR code may attempt to trigger actions, collect data or redirect users toward environments designed to harvest sensitive information.
This risk becomes particularly relevant as initiatives such as the Digital Product Passport (DPP) expand the role of QR codes as access points to product-related data. The European Commission describes the DPP as a mechanism that enables stakeholders to access standardized, reliable information about products throughout their lifecycle. Protecting the integrity of the connection between the physical product and the digital record therefore becomes essential.
Ultimately, a QR code should not be viewed as a simple hyperlink printed on a package. In modern traceability systems, it functions as a gateway to the data ecosystem behind a product. When that gateway is compromised, the risk extends beyond a single interaction and can affect the trustworthiness of the information, processes and decisions that depend on it.
Why QR Security Is a Traceability Challenge, Not Just a Cybersecurity Issue
Within modern traceability systems, QR codes are no longer simple tools for accessing information. They increasingly serve as the connection point between physical products and digital records that support transparency, compliance and supply chain visibility. In many emerging use cases, including the Digital Product Passport (DPP), the QR code functions as the user’s gateway to product data throughout its lifecycle. The European Commission describes the DPP as a digital container that enables stakeholders to access reliable and standardized information about products, materials and components.
This makes the integrity of the QR layer a strategic concern. If the point of access can be manipulated, redirected or replaced, trust in the information system itself is weakened. In other words, a traceability solution can only be as trustworthy as the mechanism that connects users to its data.
Trust Cannot Be Assumed
One of the greatest strengths of QR codes is also one of their greatest weaknesses: they are widely perceived as trustworthy. Consumers, operators and supply-chain partners often encounter them on packaging, labels, retail displays and official documentation, leading to an implicit assumption that the destination behind the code is legitimate.
However, a QR code does not inherently prove the authenticity of the content it references. Users can verify the information only after scanning, creating a trust gap at the very beginning of the interaction. In traceability environments, where users rely on product data to make informed decisions, this dependency on assumed trust introduces a significant vulnerability.
The Physical Layer Remains Exposed
Unlike many digital security controls, QR codes exist in the physical world. This means they can be tampered with using relatively simple methods. A legitimate code may be covered with a sticker, replaced entirely, reprinted elsewhere or attached to unauthorized products during distribution, storage or retail operations.
This creates a challenge that traditional cybersecurity measures alone cannot solve. While backend databases may remain secure, the physical identifier connecting a product to its digital record can become a point of manipulation. As traceability initiatives expand across increasingly complex supply chains, protecting the physical-to-digital link becomes just as important as protecting the data infrastructure itself.
The Human Factor Becomes Part of the Security Model
Even the most robust traceability architecture ultimately depends on user interaction. Whether the scanner is a consumer checking product information, a logistics operator verifying goods or a regulator accessing compliance data, every system begins with a human decision to scan a code.
This means the user effectively becomes part of the security chain. A compromised QR code can redirect a person away from verified information regardless of how secure the underlying databases, cloud platforms or traceability applications may be. As a result, organizations must view QR security not simply as a technical issue, but as a critical component of data integrity, user trust and digital transparency.
For traceability systems, the challenge is therefore broader than preventing cyberattacks. The objective is to ensure that every scan preserves the integrity of the connection between the physical product and its trusted digital identity. When that connection is protected, QR codes can fulfill their role as reliable enablers of transparency. When it is not, the credibility of the entire traceability ecosystem can be called into question.
Building Human-Centered Security into the Traceability Journey
As QR codes become a standard access point for traceability information, security can no longer be viewed solely as a technical responsibility. Every interaction begins with a human action: a consumer scanning a product label, a logistics operator verifying a shipment, or a supply chain partner accessing compliance information. In this context, the reliability of a traceability system depends not only on the integrity of the underlying data, but also on the decisions made at the moment of access.
The European Commission’s Digital Product Passport (DPP) framework is built around the idea of making trustworthy product information accessible throughout the product lifecycle. However, ensuring that users reach the correct digital record requires protecting the connection between the physical identifier and the digital information it references.
A practical approach to QR code risk awareness can help strengthen this connection and reduce exposure to manipulation or fraud.
Verify the Source Before You Scan
The first principle is simple: trust should be associated with the source, not the QR code itself. A code displayed on official packaging, corporate documentation, brand-owned channels or trusted supply chain systems is generally more reliable than one encountered through unknown or informal sources.
This reflects a broader cybersecurity principle highlighted by NIST: users should verify the origin of links and requests before interacting with them, rather than assuming legitimacy based on appearance alone.
Check for Signs of Physical Tampering
Because QR codes exist in the physical world, they are exposed to risks that purely digital assets do not face. Labels can be altered, stickers can be placed over original codes and printed materials can be replaced or redistributed without authorization.
A quick visual inspection may reveal inconsistencies that indicate manipulation. While this does not guarantee authenticity, it adds an important layer of protection, particularly in retail, logistics and warehouse environments where products pass through multiple hands before reaching the final user.
Pay Attention to Context
Fraudulent interactions often rely on urgency, pressure or unexpected requests. A QR code that promises immediate rewards, demands urgent action or directs users to provide sensitive information should be approached with caution.
Context matters. If the action requested after scanning feels unrelated to the product, service or environment in which the code appears, users should pause and verify the destination independently before proceeding. This is consistent with cybersecurity guidance that identifies urgency and pressure as common techniques used in phishing scenarios.
Trust Your Instincts When Something Feels Wrong
Technology cannot eliminate every risk. Human judgment remains an important component of security. If a QR code appears damaged, poorly placed, inconsistent with branding or simply out of context, avoiding the scan is often the safest decision.
In traceability ecosystems, this type of behavioral awareness should not be considered an optional precaution. It is part of the overall protection model that helps safeguard product information, user trust and the integrity of digital interactions.
Security Is Shared Between Systems and People
The most effective traceability systems combine secure infrastructure with informed user behavior. Robust databases, authentication mechanisms and data governance controls remain essential, but they cannot fully compensate for a compromised entry point.
For this reason, human-centered security should be viewed as a core element of modern traceability strategies. Every secure scan reinforces the connection between a product and its trusted digital identity. Every informed decision strengthens the reliability of the broader ecosystem. As QR codes continue to serve as gateways to Digital Product Passports, transparency platforms and supply chain verification systems, risk awareness becomes not just a cybersecurity practice, but a fundamental requirement for data integrity and trust.
From QR Code Deployment to QR Code Governance
Implementing QR codes is relatively simple. Ensuring that they remain trustworthy over time is considerably more complex. As QR codes become a critical component of traceability systems, organizations must move beyond basic deployment and adopt a governance model that protects the integrity of the connection between physical products and digital information.
This challenge is becoming increasingly relevant as QR codes are used to provide access to sustainability data, compliance information and Digital Product Passports (DPPs). Because these identifiers act as gateways to product data, organizations must ensure that users are consistently directed to authentic, controlled and reliable digital environments. The European Commission highlights the importance of providing standardized and trustworthy product information through the DPP framework, making the reliability of the access mechanism a fundamental requirement.
Use QR Codes with a Clear Purpose
Not every interaction requires a QR code. Organizations should avoid treating them as a default solution and instead deploy them where they create genuine value for users, whether supporting product transparency, supply chain verification or access to compliance-related information.
A purposeful approach reduces unnecessary exposure points while helping users better understand when a QR code is a legitimate part of a traceability process. In practice, effective governance begins with asking a simple question: does the QR code solve a real information or verification need?
Ensure Every Destination Is Trusted and Controlled
A QR code is only as trustworthy as the destination it references. For this reason, organizations should ensure that all codes are resolved exclusively to official domains, authenticated platforms and controlled digital infrastructures.
Users should never have to guess whether they have reached the correct destination. Consistent domain naming, secure connections and transparent ownership contribute to a more reliable user experience while reducing opportunities for fraud and impersonation.
This principle is aligned with established cybersecurity guidance that emphasizes the importance of verifying the legitimacy of digital destinations before interacting with them.
Make Legitimate Interactions Easy to Recognize
Technology alone cannot create trust. Organizations must also communicate clearly with users.
Consumers, operators and supply chain partners should understand where a QR code will lead, why it is being used and how legitimate interaction should appear. The more predictable and transparent the experience, the easier it becomes to identify anomalies and suspicious behavior.
In traceability ecosystems, user awareness is not merely an awareness initiative; it is an essential component of risk management. Clear communication helps strengthen confidence in the system while reducing dependence on assumptions.
Protect the Physical-to-Digital Link
Because QR codes exist in both physical and digital environments, they require protection on multiple levels. A secure governance strategy should include measures designed to reduce the risk of substitution, replication or manipulation.
Depending on the use case, organizations may adopt secure labeling technologies, dynamic QR codes that incorporate validation mechanisms or integrations with authentication and verification systems. These approaches help ensure that scans continue to lead to the correct digital resource even when products move through complex supply chains or retail environments.
The objective is not simply to secure the code itself, but to preserve the integrity of the physical-to-digital connection that underpins traceability.
Governance Is the Foundation of Trust
Ultimately, the success of a traceability ecosystem depends on more than data quality. It depends on users being able to trust that the information they access is genuinely linked to the product in front of them.
For this reason, QR codes should be governed as strategic digital assets rather than treated as static labels. A combination of controlled usage, verified destinations, transparent communication and anti-tampering measures helps create a more resilient and trustworthy ecosystem. When these elements work together, QR codes can fulfill their intended role: providing secure access to a product’s trusted digital identity while preserving the integrity of the information that supports transparency, compliance and traceability.
QR Codes as Trust Infrastructure in the Digital Product Era
For many organizations, QR codes are still perceived as a practical tool: a simple way to connect a physical item to digital information. Yet as traceability systems evolve, their role is becoming far more strategic. QR codes increasingly serve as the interface through which consumers, regulators, supply chain partners and service providers access information related to product origin, composition, sustainability, compliance and circularity.
This shift is particularly evident in initiatives such as the Digital Product Passport (DPP), where the connection between the physical product and its digital record becomes a fundamental requirement. According to the European Commission, the DPP is intended to provide access to reliable, standardized product information throughout the product lifecycle, supporting transparency, sustainability and regulatory compliance.
But the strategic importance of QR codes extends beyond today’s traceability requirements: the retail and consumer goods industries are currently preparing for GS1 Sunrise 2027, a global initiative aimed at enabling point-of-sale systems worldwide to read and process next-generation 2D barcodes, including QR codes and GS1 DataMatrix symbols. The initiative reflects a broader recognition that traditional one-dimensional barcodes can no longer satisfy the growing demand for product transparency, traceability, and digital engagement.
Unlike conventional barcodes that primarily identify a product through a GTIN, GS1-compliant QR codes can support access to a much richer set of information, including batch numbers, expiration dates, product origin, sustainability attributes, regulatory information, and links to Digital Product Passports. This transforms the barcode from a simple product identifier into a gateway to a product’s digital identity.
For traceability initiatives, the implications are significant: a single standardized QR code can support multiple stakeholders simultaneously, from consumers seeking product transparency to manufacturers verifying authenticity, logistics providers tracking product movement, and regulators assessing compliance. By creating a common access point for trusted information, Sunrise 2027 has the potential to strengthen end-to-end visibility across increasingly complex supply chains.
However, the transition also reinforces the central argument of this article: a QR code alone cannot create trust. As QR codes become the primary interface between physical products and digital information ecosystems, organizations must ensure that the underlying data, governance processes, authentication mechanisms, and digital infrastructure are equally robust. The future of product identification will depend not only on making information accessible, but on ensuring that every scan leads to reliable, authentic, and trustworthy data. In the age of Digital Product Passports and connected supply chains, QR codes are evolving from simple labels into critical components of the trust architecture that underpins modern traceability.
In this context, a QR code should not be viewed as a graphic element printed on a package. It functions as a trust interface between a physical object and its digital identity.